CRA Reporting Obligation (Cyber Resilience Act)

 06.10.2026

 Consulting, Cybersecurity
Imagine a Saturday morning at 7:15 a.m. A trusted Computer Security Incident Response Team (CSIRT) tells you that a software component in your connected industrial gateway is already being exploited by attackers. Under the Cyber Resilience Act (CRA), the deadline for your early warning expires on Sunday at 7:15 a.m., and nobody asks whether Monday is a public holiday.
In short: Since September 11, 2026, manufacturers of products with digital elements have to report actively exploited vulnerabilities and severe security incidents. The early warning is due within 24 hours, the notification within 72 hours, and the final report after that. Reports are submitted through the Single Reporting Platform (SRP) of the EU Agency for Cybersecurity (ENISA). In Germany, CERT-Bund at the Federal Office for Information Security (BSI) is the competent CSIRT.
The form is the smallest part of the task. What matters is whether, within a few hours, you know which products and versions are affected, who may approve the report, and since when you have known about the problem. This article shows what the obligation requires, what a process for the first 24 hours can look like, and what you should prepare now.
Talk to us if you would like to assess your company’s reporting readiness together: To our cybersecurity consulting
What Has Applied Since September 11, 2026
What Has Applied Since September 11, 2026
The reporting obligations under Article 14 CRA apply roughly 15 months before the remaining manufacturer obligations, which take effect on December 11, 2027. They cover two events: an actively exploited vulnerability for which there is reliable evidence of malicious exploitation, and a severe security incident that affects product security. A proof of concept or a high severity rating alone does not trigger the obligation.
Reporting runs in three stages:
| Stage | Deadline | Content (selection) |
|---|---|---|
| Early warning | without undue delay, at the latest 24 hours after becoming aware | first details on the event and the product; for vulnerabilities, the Member States concerned |
| Notification | at the latest 72 hours after becoming aware | nature of the vulnerability or incident, corrective or mitigating measures taken or recommended |
| Final report | vulnerability: 14 days after a corrective or mitigating measure is available; incident: one month after the 72-hour notification | severity, impact, information on the threat actor and on the security update |
Two points are often overlooked. The obligation also applies to legacy products that were already on the market before December 11, 2027. In addition, under Article 14(8) you have to inform affected users yourself; the report to the authority does not replace this.
The obligation applies directly under the EU regulation. The fact that the German implementing act for the CRA was still going through parliament in early October 2026 does not postpone it. Violations of Article 14 can result in fines of up to 15 million euros or 2.5 percent of worldwide annual turnover.
When the Clock Starts Ticking
What matters is the manufacturer's awareness. According to the European Commission’s interpretation, this is the case as soon as a prompt initial assessment yields a reasonable degree of certainty. The assessment must not be delayed in order to postpone the report. The guidance is not legally binding, but it shows how the Commission reads the provision.
A practical rule follows: every case in the vulnerability process needs a documented timestamp for the receipt of the information, its source and the time of classification. As things stand, the SRP does not fully capture this point in time. Its counter for the 72-hour notification currently runs from the submission of the early warning, not from awareness. You are therefore better off calculating the statutory deadline yourself; ENISA has announced a correction.
Does the Obligation Apply to Your Product?
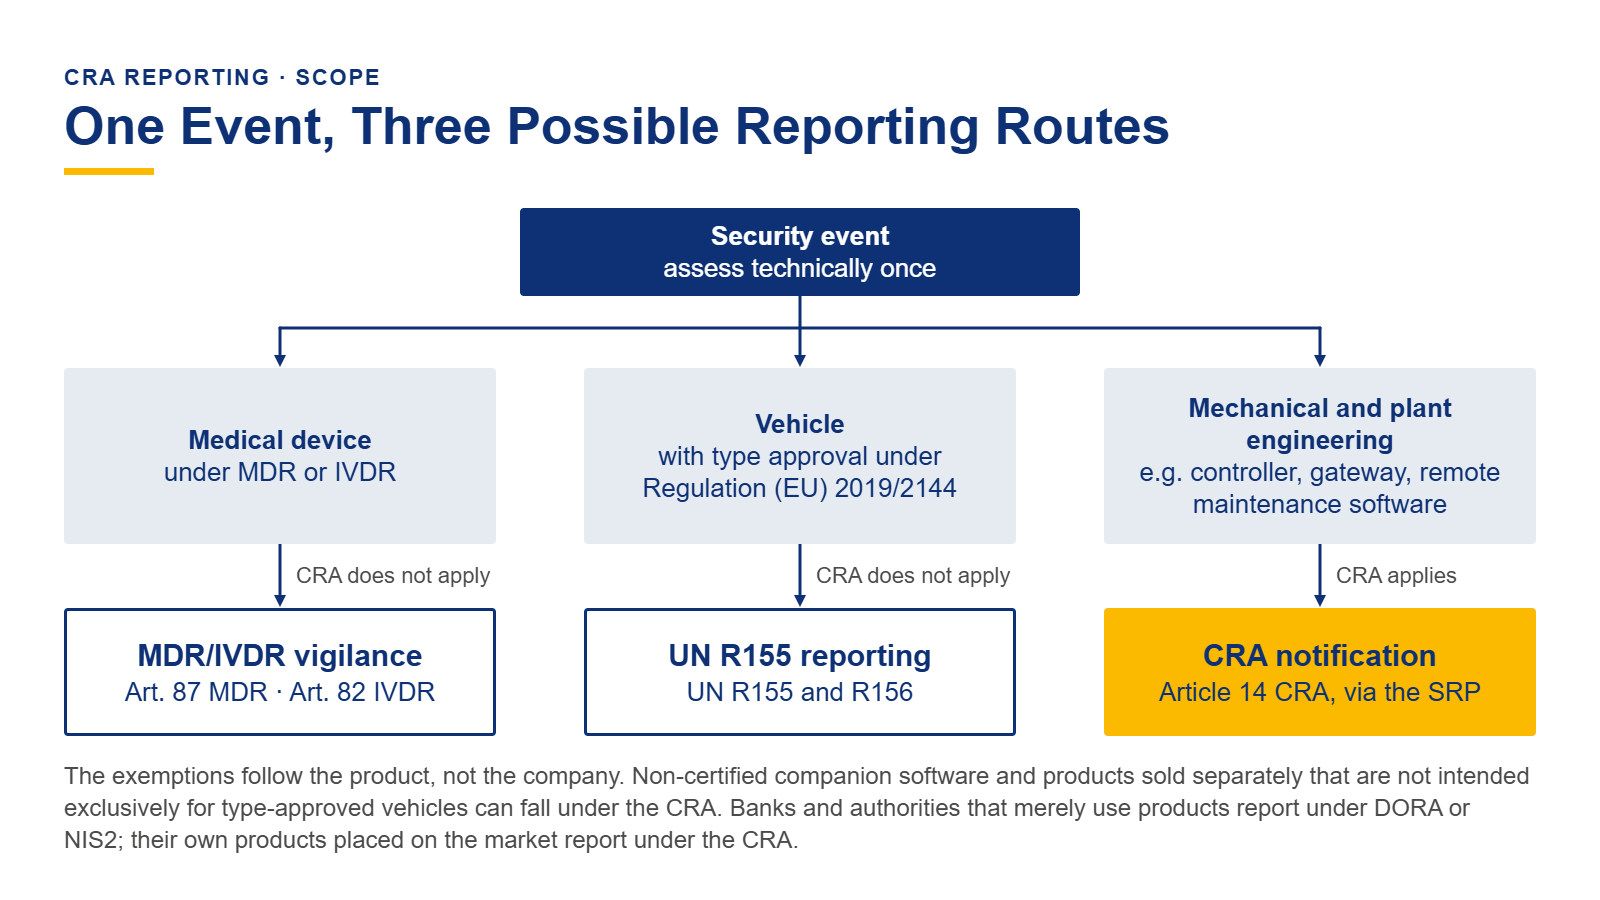
The exemptions follow the product, not the company. The same company can have one product outside and another inside the scope of the CRA.
- Medical technology: Products under the Medical Device Regulation (MDR) and the In Vitro Diagnostic Regulation (IVDR) are excluded; vigilance under Article 87 MDR and Article 82 IVDR respectively applies. Non-certified companion software, for example for hospital administration, remains in scope. In December 2025, the Commission proposed a dedicated cyber reporting procedure within the MDR and IVDR, which is not yet applicable law.
- Automotive: Vehicles covered by type approval under Regulation (EU) 2019/2144 are excluded. UN R155 and R156 apply there. Products made available separately on the market that are not intended exclusively for type-approved vehicles can fall within scope. This has to be checked case by case.
- Mechanical and plant engineering: There is no general exemption. Controllers, gateways and remote maintenance software fall under Article 14. The Machinery Regulation (EU) 2023/1230 applies in addition from January 20, 2027 and does not replace the CRA.
- Financial sector and public administration: The CRA contains no exemption for these sectors; what matters is the role. Anyone who places software or connected devices for banks, insurers or public authorities on the market, such as banking software, payment terminals or specialist administrative applications, is a manufacturer and subject to Article 14. Banks and authorities that merely use such products are not addressees of the CRA. They have their own reporting channels: in the financial sector under the Digital Operational Resilience Act (DORA), in public administration under the NIS2 Directive, insofar as the entity is covered by it. According to the wording of the regulation, in-house developments for internal use are not covered either, because the CRA only applies to products supplied in the course of a commercial activity. Where authorities pass software on to other bodies, this has to be assessed case by case. Software that users only consume as a cloud service is, as a rule, outside the CRA according to the Commission guidance. The German Banking Industry Committee calls for an exemption for companies under DORA, but this is not applicable law so far.
Anyone working in several of these worlds should set up a joint triage: a case is assessed technically once and then branches into MDR or IVDR vigilance, UN R155 reporting or CRA notification. You will find more background in our articles on preparing for the EU Cyber Resilience Act and on the Cyber Resilience Act in medical technology.
The First 24 Hours: A Practice Scenario
The following scenario is an elaboration based on the sources cited, not an official template. The times are internal safety margins, not statutory interim deadlines. Starting point: a machine manufacturer supplies a remote maintenance gateway in several firmware lines in 14 EU Member States; it contains an open-source web server library.
| Time | Event | Decision |
|---|---|---|
| Sat 7:15 a.m. | CSIRT notice arrives in the product security mailbox | Open case, secure timestamp, activate on-call duty |
| by 8:30 a.m. | Query Software Bill of Materials (SBOM) and product inventory | List: version included, not included, unknown |
| by 11:00 a.m. | Development checks whether the vulnerability is exploitable in the product | Record result per firmware line |
| by 11:30 a.m. | Decision point: reportable yes or no | Log decision with reasoning and timestamp |
| by 2:00 p.m. | Determine affected countries and variants, activate Assigned Representative | Define competent CSIRT and product scope |
| by 5:00 p.m. | Define workaround, prepare customer information under Article 14(8) | Approval by the reporting decision-maker |
| by 8:00 p.m. | Submit early warning in the SRP | Archive reference number, buffer to the deadline: eleven hours |
| Sun 12:00 a.m. - 7:15 a.m. | Situation meeting, plan for the 72-hour notification | Patch plan per firmware line |
An exercise only becomes meaningful once you inject disruptions: the Primary Assigned Representative is on vacation or has lost the device for multi-factor authentication. The supplier does not respond for six hours. No SBOM exists for a legacy product. Afterwards, check how long it took to reach documented awareness, whether the version list was correct, and whether the buffer to the 24-hour limit was larger than six hours.
If you would like to run through such a scenario for your product portfolio, talk to us.
Five Prerequisites That Must Be in Place Before an Incident
- Decision authority and availability – A named person may decide "reportable yes or no", with a deputy and 24/7 availability, including on regional public holidays. Approval by the management board does not belong on the critical path.
- SRP access – Reports are submitted through personal EU Login accounts with multi-factor authentication. Set up one Primary and at least two Secondary Assigned Representatives in advance. Note that the platform offers no interface (API) and initially runs in English only. Drafts are visible only to their creators, so the texts should be prepared in the incident team's shared document.
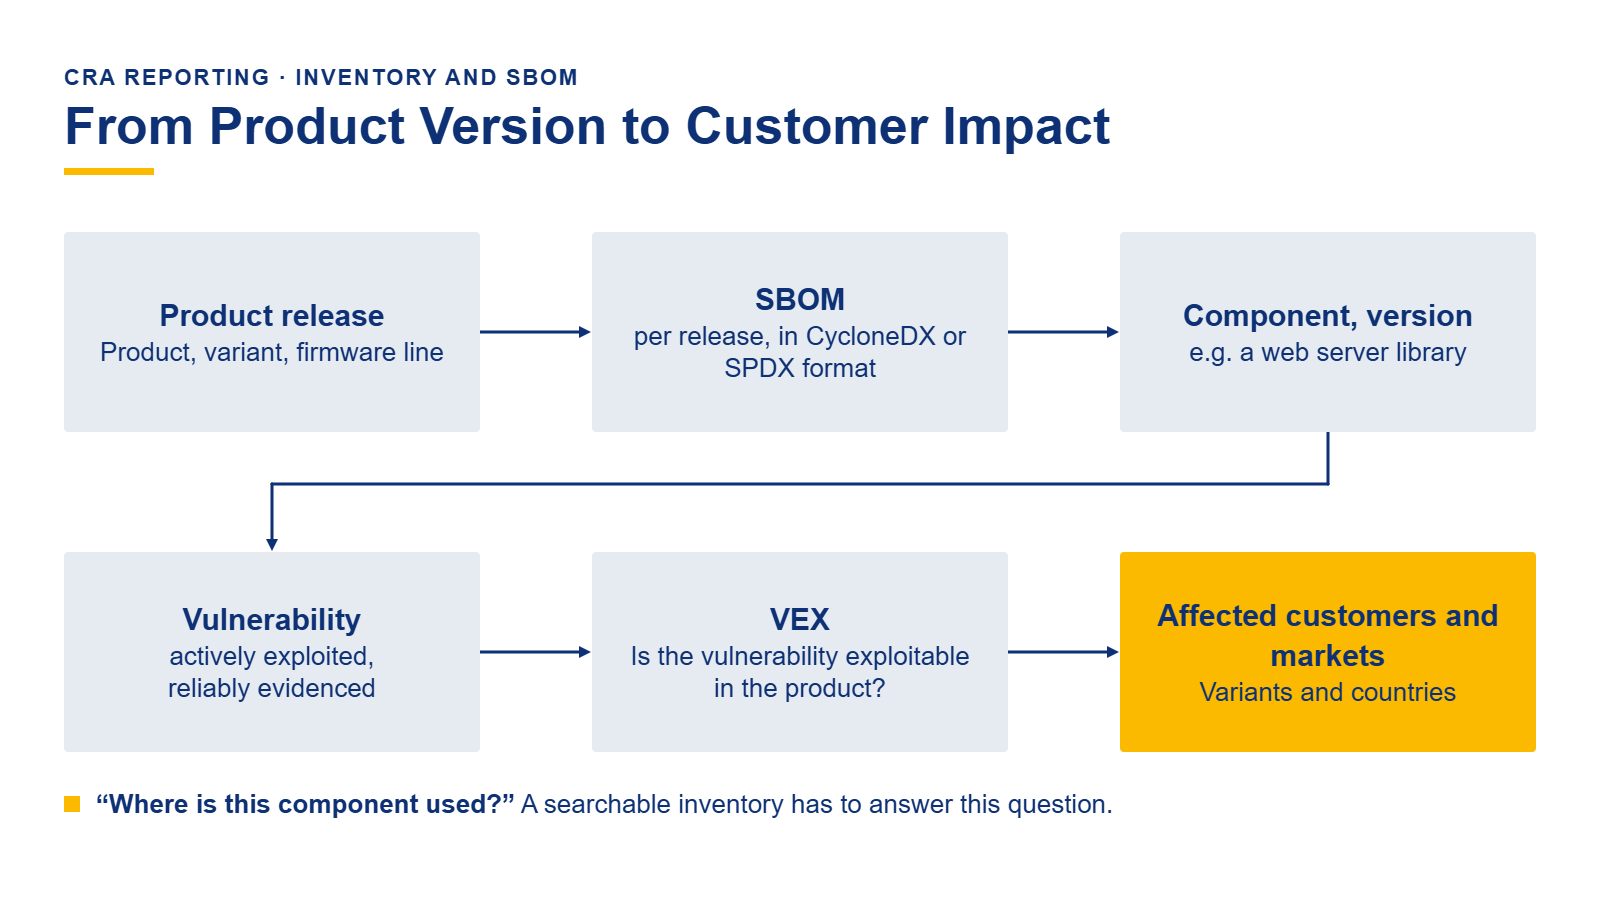
- Inventory and SBOM – The question “Where is this component used?” has to be answered by a searchable inventory that maps components and versions to products, variants and markets. In Technical Guideline TR-03183, the BSI describes requirements for SBOMs in CycloneDX or SPDX format. With Vulnerability Exploitability eXchange (VEX), you document that a vulnerability is not exploitable in the product.
- Vulnerability process and suppliers – A Product Security Incident Response Team (PSIRT) or a comparable function in line with ISO/IEC 30111 and ISO/IEC 29147 receives reports, assesses them and decides on disclosure. The BSI also recommends a findable security contact and a security.txt file. Supplier contracts should include a security contact, a notification period well under 24 hours, and the delivery of SBOMs per release.
- Legacy products first – Installed products with a network connection are already subject to reporting today, even if the build environment and development team no longer exist. Start with an inventory by risk and installed base.
What Is Still Open After the First Weeks
We say it openly: after a good three weeks, there is hardly any robust practical experience. ENISA and the BSI have so far published neither reporting figures nor evaluations, and no supervisory practice on Article 14 is yet discernible. Statements about what authorities “accept in practice” cannot currently be substantiated.
The starting position before launch was mixed. In a Bitkom survey of 1,003 companies, 29 percent said they knew what the CRA means for them. Still open are also the line between a tip-off and “reasonable certainty”, the required depth of evidence for third-party components, and the interplay with NIS2: an entity that falls under NIS2 can trigger two reports with similar deadlines for the same event. The Commission has proposed simplifications, which are not yet applicable law. The platform keeps changing, so check the ENISA FAQ regularly.
Conclusion: A Process That Works at the Weekend
The litmus test of Article 14 is whether your company can answer five questions within a few hours of an external tip-off:
- Which products are affected?
- Are the conditions met?
- Since when have we known?
- What do users have to do now?
- Who reports what to whom?
That only works if vulnerability management, SBOM, supplier management, regulatory affairs and communications work as one process.
The good news: much of this can be prepared, and an exercise reveals the gaps faster than any document review. If you are looking for a sparring partner, you will find in us experience from developing and securing safety-critical software in regulated industries. Talk to us!
FAQ
The BSI states that prior registration is not required. Set up the EU Login accounts with multi-factor authentication in advance anyway, so that you do not lose time in an emergency.
Yes. Article 69(3) exempts the reporting obligations from the transitional rule for legacy products. What matters is that the product is within scope and still on the market.
No. Reportable are actively exploited vulnerabilities with reliable evidence that are contained in your product and exploitable there. Also document negative decisions.
Products under the MDR, the IVDR or vehicle type approval are excluded. Software or components sold separately can still be affected.
Products under the MDR, the IVDR or vehicle type approval are excluded. Software or components sold separately can still be affected. There is no exemption for the financial sector and public administration: manufacturers of products for these sectors report under Article 14, mere operators do not.
No. You also have to inform affected users yourself about the vulnerability and countermeasures.
Sources
- Bitkom e. V. (2026, September 10). Cyber Resilience Act: Nur 3 von 10 Unternehmen sind vorbereitet [in German].
- Bundesamt für Sicherheit in der Informationstechnik. (2026, September 11). Cyber Resilience Act: Meldepflicht startet [press release, in German].
- Bundesamt für Sicherheit in der Informationstechnik. (2026). CRA Single Reporting Platform [in German].
- Die Deutsche Kreditwirtschaft. (2026, April 1). Comments on the Commission guidance on the application of the Cyber Resilience Act (CRA).
- European Commission. (2026). Cyber Resilience Act: Reporting obligations.
- European Commission. (2026, July 27). Guidance on the application of the Cyber Resilience Act, C(2026) 5252.
- European Parliament & Council of the European Union. (2017). Regulation (EU) 2017/745 on medical devices (MDR), in particular Art. 87.
- European Parliament & Council of the European Union. (2017). Regulation (EU) 2017/746 on in vitro diagnostic medical devices (IVDR), in particular Art. 82.
- European Parliament & Council of the European Union. (2023). Regulation (EU) 2023/1230 on machinery.
- European Parliament & Council of the European Union. (2024). Regulation (EU) 2024/2847 (Cyber Resilience Act), in particular Art. 2, 3, 14, 64 and 69.
- ENISA. (2026). CRA Single Reporting Platform: Frequently Asked Questions (updated October 3, 2026).
- FIRST. (n.d.). PSIRT Services Framework, Version 1.1.
- VDMA. (2026). CRA Vulnerability Handling Guideline.